davis@portfolio:~$ whoami
Davis Barillas — Forward Deployed Engineer · AI security, identity & integrations · game dev (PixelYeti)
davis@portfolio:~$ ./portfolio --interactive
Select a section — use ↑/↓ and Enter:
[↑/↓] navigate · [enter] open · click also works · switch to GUI up top
davis@portfolio:~$ ▮
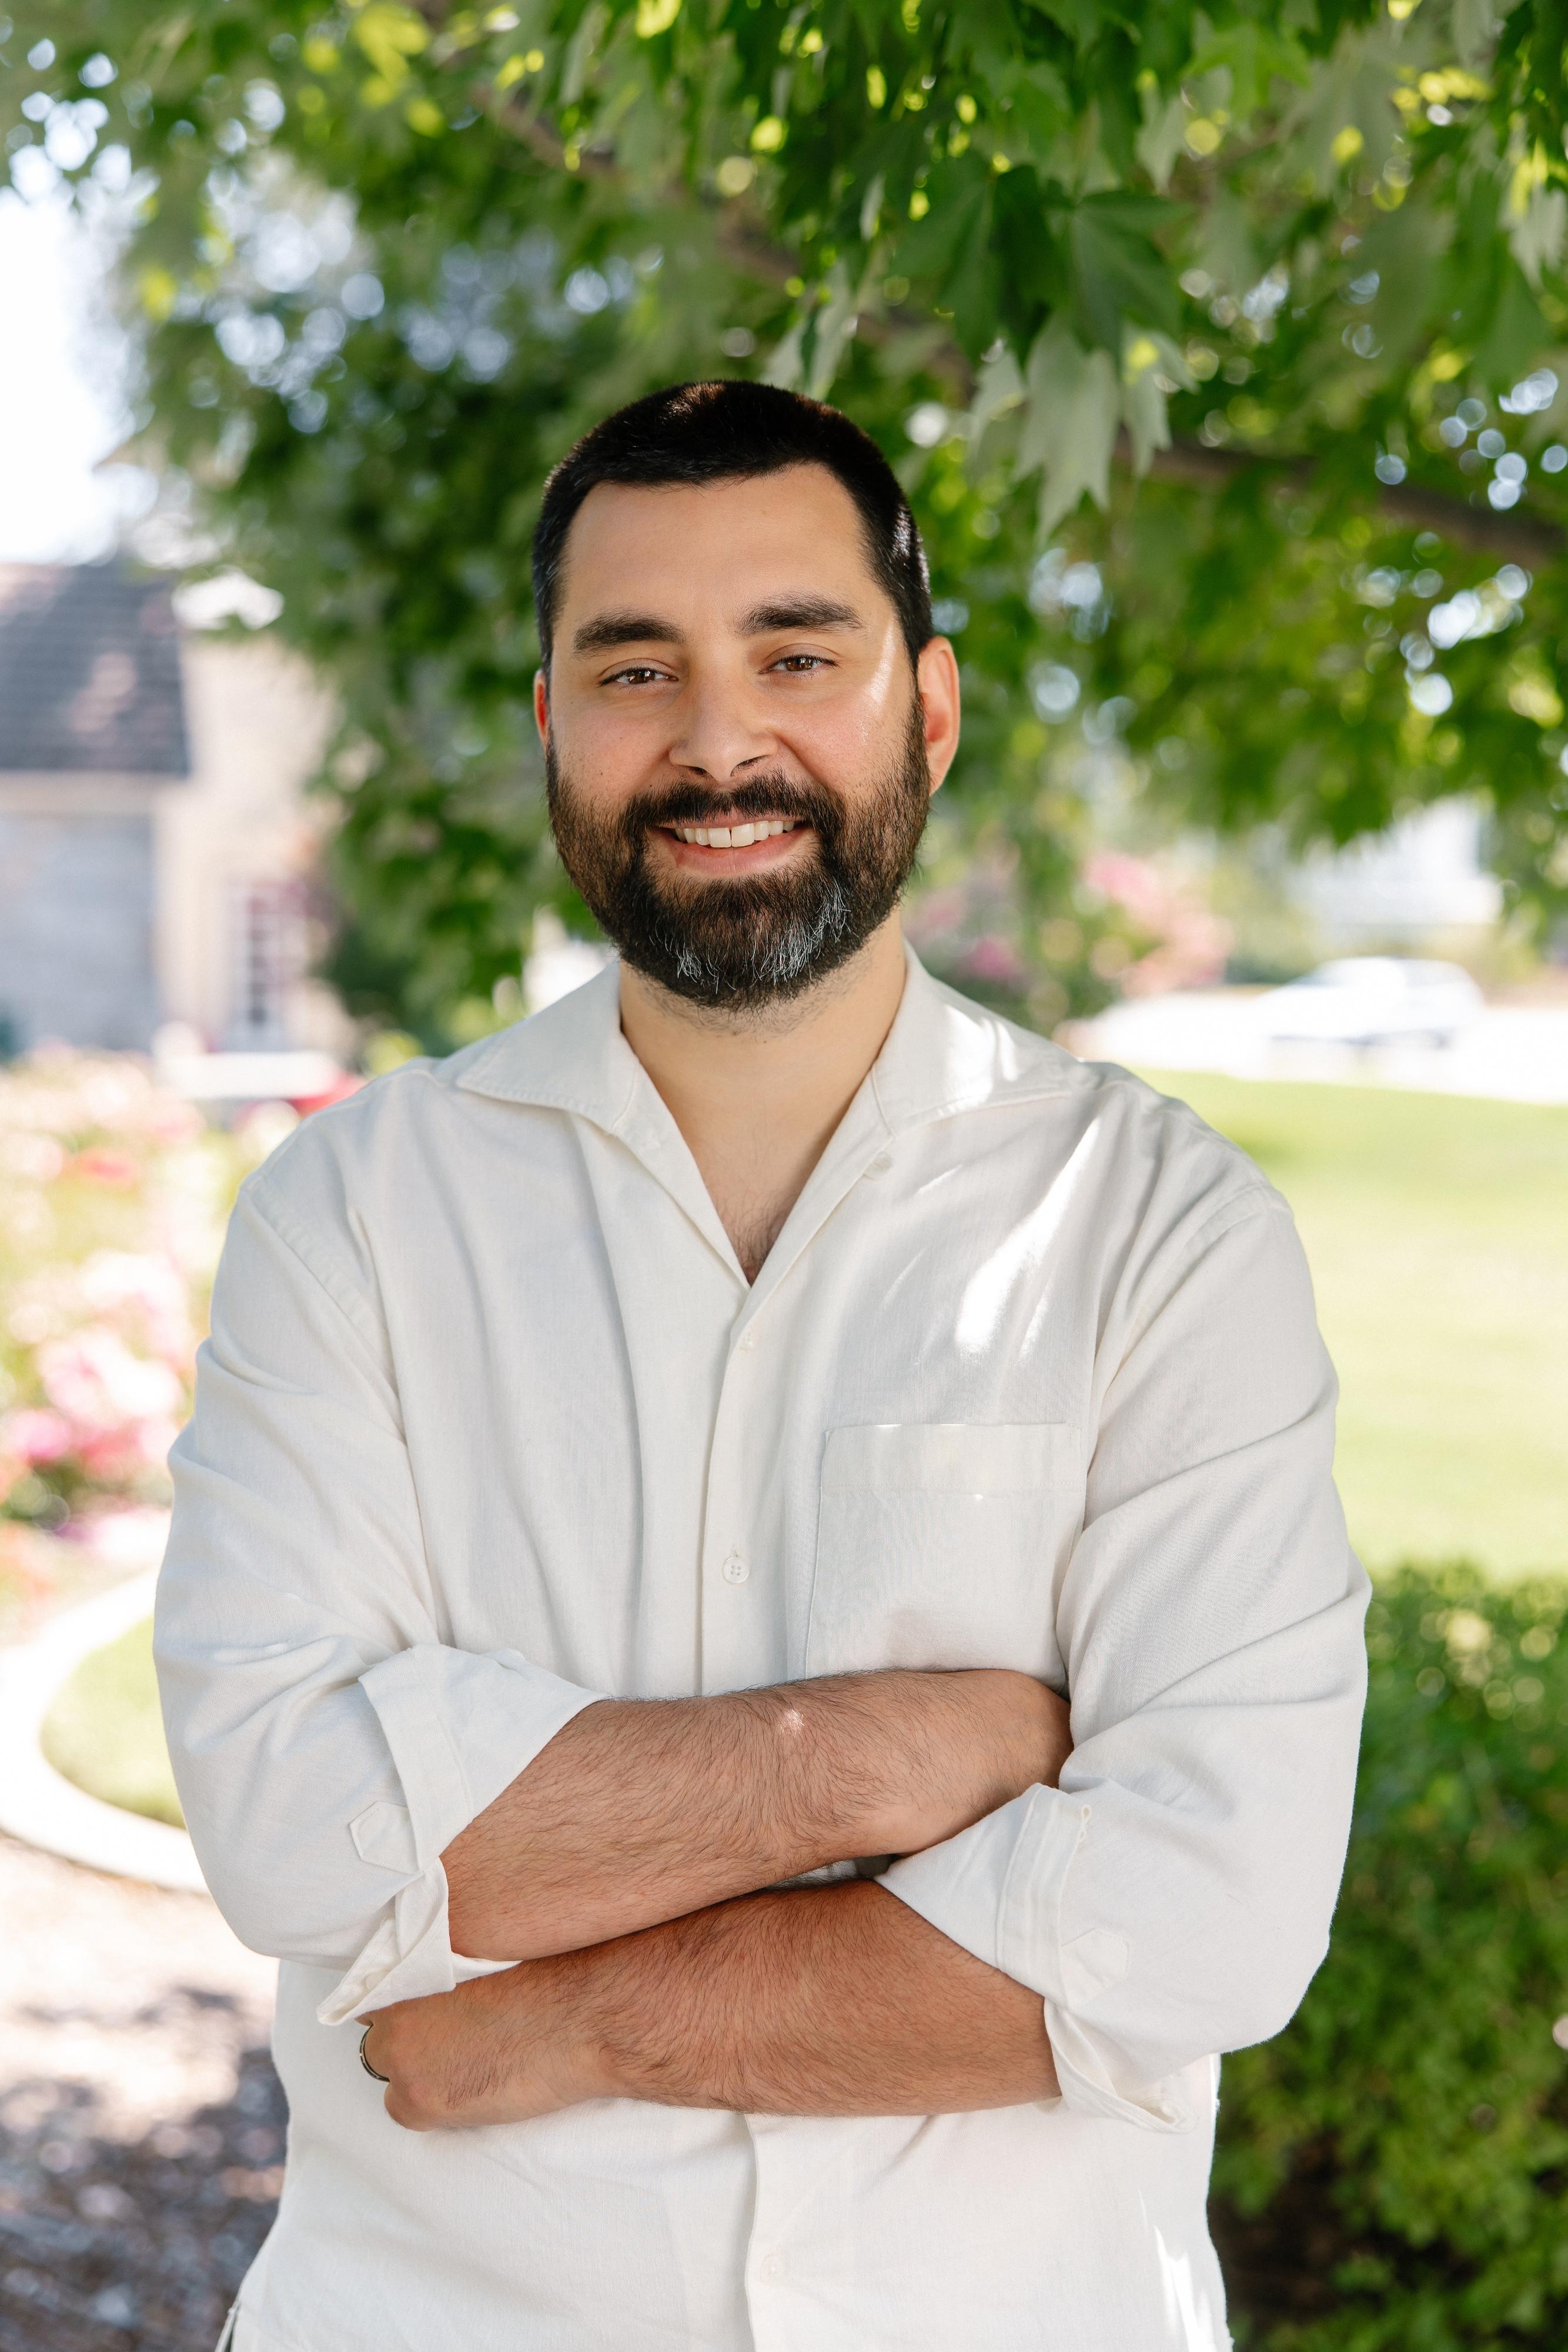
Hi, I'm Davis Barillas
I ship solutions to
hard technical problems
Forward Deployed Engineer across security, cloud, and integrations — and a game developer building in Unity & C#. I like shipping things, whether it's security tooling or games.
- TypeScript
- Python
- C#
What I do best
I make customer success teams AI-native
I've spent years inside customer success and customer engineering orgs — leading teams, owning the hardest accounts, and shipping the integrations that make enterprise deployments actually stick. Now I deploy enterprise AI security for a living. I bring both halves together: re-architecting customer success and support around AI agents and automation — securely, and all the way into production.
AI agents for CS & support
Design and deploy agentic workflows that deflect tickets, draft responses, and surface account risk — grounded in real customer-success experience, not theory.
Secure by default
Every AI deployment ships with guardrails: prompt-injection defense, data controls, and runtime policy — straight from my day-job AI security work.
Forward-deployed delivery
I embed with your team, wire into your stack and data, and drive it to production. You get working software in your environment, not a slide deck.
Technical Skills
A practical, hands-on toolset
Tools and domains I work with across AI security, application security, cloud integrations, and developer platforms.
Software Engineering
- TypeScript
- React / Next.js
- Full-Stack Web
- REST APIs
- System Design
- Testing
AI Security & Agents
- LLM Agent Security
- Runtime Guardrails
- Prompt Injection
- Red Teaming
- MCP
- Model Gateways
AppSec & DevSecOps
- SAST
- SARIF
- Vulnerability Triage
- Secure CI/CD
- Semgrep
- SOC 2
Cloud, APIs & Identity
- REST APIs
- SAML / SSO
- Okta
- OAuth
- AWS Bedrock
- Azure
Languages & Tooling
- Python
- FastAPI
- Docker
- GitHub / GitHub Actions
- GitLab
Game Development
- C#
- Unity
- Gameplay Systems
- Roguelite / Deckbuilder
- Game Design
- Prototyping
Spoken Languages
- English (Native)
- Russian (Native)
Featured Projects
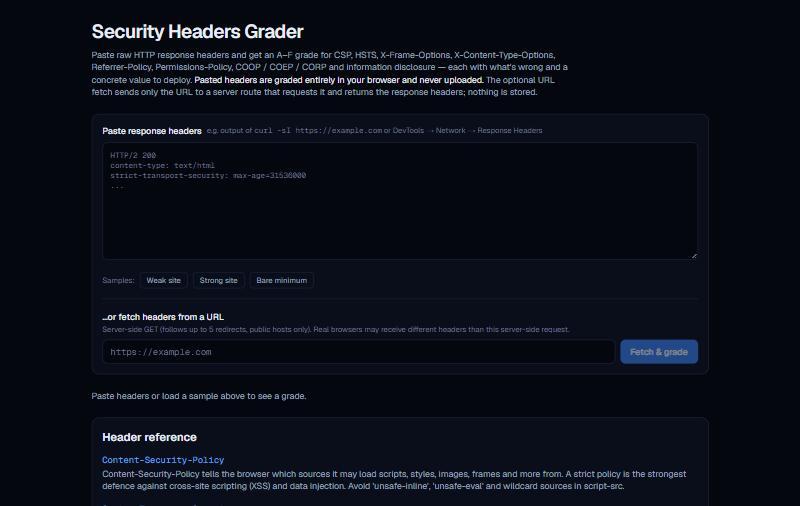
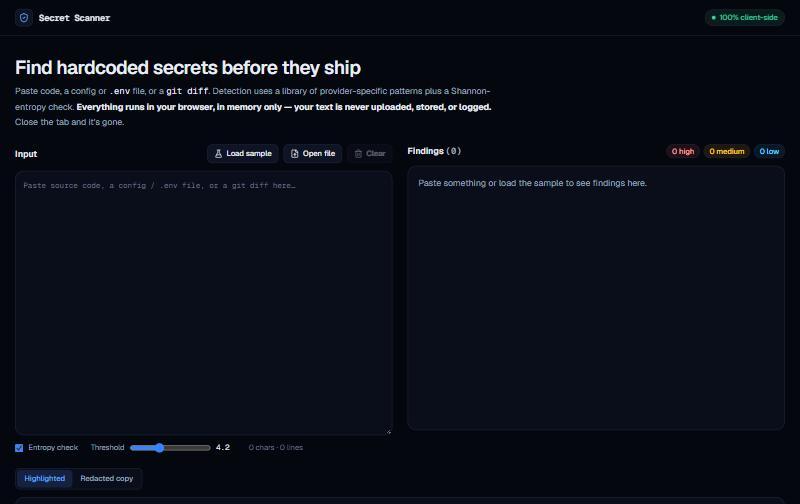
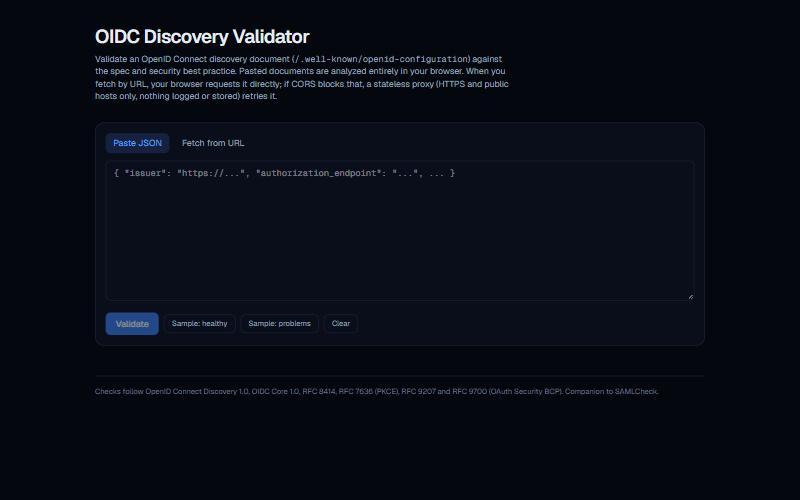
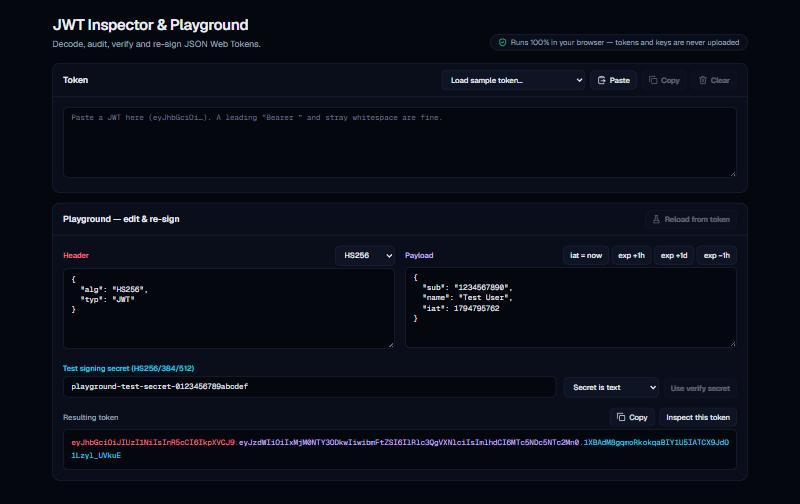
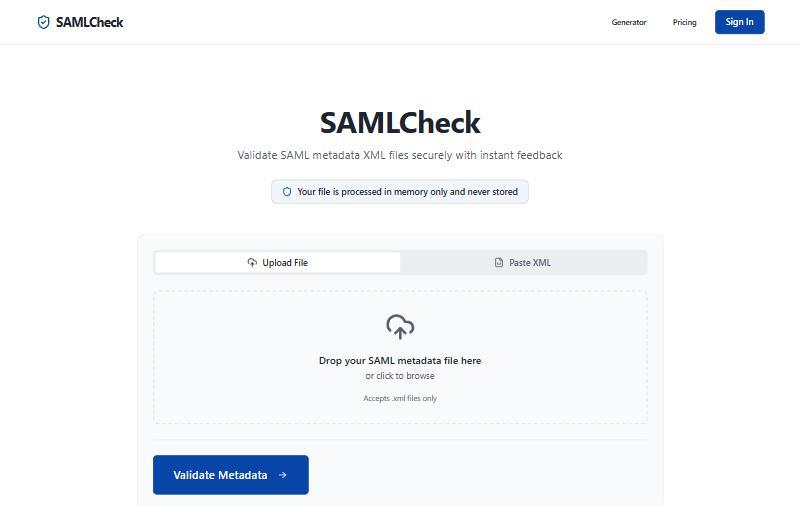
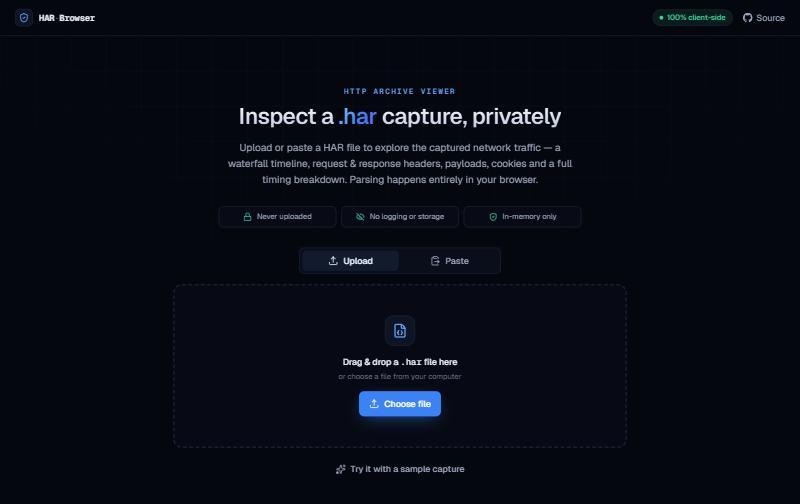
Tools I've built & shipped
Security and developer tools you can actually use — live, privacy-first, and built to work — plus a couple of games on the side.
Experience
Professional background
A decade across IT operations, application security, and forward deployed engineering.
Forward Deployed Engineer · Straiker
April 2026 – November 2026
Sunnyvale, CA · Remote
- Partner directly with enterprise customers to deploy and operationalize AI security across real-world AI/ML stacks — LLMs, agentic systems, and developer workflows — owning each engagement end to end.
- Lead end-to-end implementations: scope the customer's architecture, build custom integrations via REST APIs and CI/CD pipelines, and embed the platform where their AI actually runs.
- Design and tune runtime guardrails that protect against prompt injection, data exfiltration, and agent misuse — balancing strong security with developer velocity.
- Run hands-on adversarial testing and red-teaming of enterprise AI applications to surface and close real attack paths before they reach production.
- Integrate security controls across AWS Bedrock, Azure, model gateways, MCP, and Claude Code hooks, meeting customers in the environments and toolchains they already use.
- Investigate and resolve deployment issues across authentication errors, API failures, timeouts, rate limits, and unpredictable agent execution behavior.
- Act as the technical bridge between customers and Straiker's Product and Engineering teams, translating field needs into concrete product and roadmap improvements.
- Operate with high ownership in fast-moving, ambiguous environments, securing AI systems at enterprise scale.
Senior Technical Account Manager · Semgrep
September 2025 – April 2026
San Francisco, CA · Remote
- Served as the senior technical owner for enterprise customers adopting, scaling, and maximizing value from Semgrep's application security platform.
- Partnered with security and engineering teams to integrate Semgrep into CI/CD pipelines and developer workflows across GitHub and GitLab.
- Led onboarding, enablement, and best-practice rollouts so teams could stand scanning up quickly and adopt it sustainably.
- Triaged findings, fine-tuned detection rules, and aligned security coverage to each customer's codebase and risk tolerance — cutting false positives and sharpening signal.
- Troubleshot scan failures, authentication, and API integration issues, keeping security programs running smoothly.
- Served as a trusted technical advisor, driving customer outcomes, retention, and expansion.
- Acted as the voice of the customer internally, surfacing field feedback to influence Semgrep's product direction and roadmap.
Customer Success Engineer Team Lead · ArmorCode
December 2022 – August 2025
Remote
- Led and mentored a team of Customer Success Engineers supporting enterprise application security platforms across AppSec, cloud, and infrastructure security.
- Owned the most complex, high-priority accounts and served as the escalation point for the hardest technical issues.
- Debugged integrations spanning SAML/SSO, REST APIs, and third-party connectors — Jira, ServiceNow, Tenable, and CrowdStrike — stitching scanners, APIs, and vulnerability management systems together end to end.
- Troubleshot connector failures, data-ingestion breakages, authentication, and remediation workflows to keep customer programs running.
- Drove process improvements across onboarding, ticket triage, and training that reduced time-to-value and lifted customer satisfaction.
- Coordinated technical escalations between customers and engineering, driving hard issues to resolution.
- Partnered with Product and Engineering to relay customer feedback and influence roadmap prioritization.
- Mentored engineers, built internal documentation and onboarding resources, and accelerated new-hire ramp-up.
- Championed adoption and engagement, contributing to retention, renewals, and expansion through proactive success planning.
Senior Customer Success Engineer · Qwiet.ai / ShiftLeft
October 2021 – December 2022
Santa Clara, CA · Hybrid
- Served as the primary technical advisor for enterprise customers on ShiftLeft's code analysis and application security platform — onboarding, deployment, and strategy.
- Drove adoption of automated static analysis and CI/CD integrations (Jenkins, GitHub, GitLab) for early vulnerability detection and faster DevSecOps workflows.
- Led deep-dive sessions with security and engineering teams to optimize scanning policies, triage findings, and wire results into developer pipelines.
- Built scripts, dashboards, and technical resources that streamlined support and improved client self-sufficiency.
- Troubleshot pipeline integrations, API configurations, and developer remediation workflows.
- Partnered with Engineering and Product to report bugs, shape roadmap priorities, and advocate for customer use cases in dynamic AppSec environments.
- Mentored junior CSEs and improved customer onboarding, documentation, and internal tooling.
IT Analyst · Upstart
November 2016 – October 2021
San Mateo, CA · On-site
- Delivered Tier 1 and Tier 2 support across a fast-scaling fintech, resolving hardware, software, and access issues for 500+ employees.
- Owned onboarding and offboarding end to end — account provisioning, SSO setup, and hardware deployment across macOS and Windows.
- Administered core SaaS platforms including Google Workspace, Okta, Slack, Zoom, and Jira, and built automations and access controls that improved security and efficiency.
- Partnered with Security and Engineering to investigate access anomalies, support audits, and enforce IT compliance policies including SOC 2.
- Led process improvements in ticket triage, hardware inventory, and asset lifecycle management that cut IT resolution time by 25%.
- Supported office network infrastructure, A/V systems, and remote collaboration tools to keep hybrid teams productive.
- Grew with the company through a period of rapid scaling, taking on broader IT and security responsibilities over five years.
Writing
Notes from the field
Deep dives on the security and identity tools I build — how they work and what I learned shipping them.
Open to new roles
I'm actively exploring new roles across forward deployed & solutions engineering, technical account & customer success, and AI / application security. Based in San Francisco, California — the quickest way to reach me is email, or find me on LinkedIn.